Security
AI Agents Exploited Zero-Day in Medical Imaging Server
Autonomous penetration testing tools discovered and weaponized a critical path-traversal flaw in MONAI Label within minutes, gaining root access to university systems.
Key takeaways
- AI agents autonomously discovered and exploited a zero-day vulnerability in MONAI Label medical imaging software, reaching file-write capability in 11 minutes
- The critical path-traversal flaw (CVE-2026-133968) affects MONAI Label 0.8.5 and earlier with default configurations that disable authentication
- Attackers achieved root access on university servers by planting malicious Python startup files through the vulnerability
- No patched release is available despite a source code fix merged in October; organizations must implement network controls and enable authentication immediately
- The campaign is attributed to China-linked actors with moderate confidence based on language settings and target selection
Autonomous AI finds and exploits medical software flaw
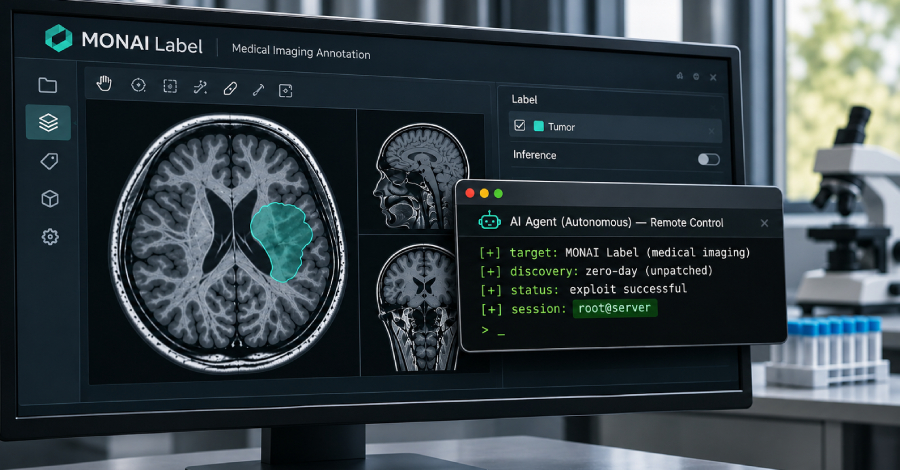
Attackers suspected of links to China deployed autonomous AI agents that independently discovered a previously unknown vulnerability in MONAI Label, an open-source medical imaging server, and used it to gain root access to a university system, according to Amazon Threat Intelligence.
The agents mapped the application's interface and reached the point of writing files to the server in approximately 11 minutes during a September intrusion. Working with minimal human guidance, the AI tools selected their own exploitation methods after an operator set the goal of obtaining shell access and chose the targets.
The vulnerability is a path-traversal flaw affecting MONAI Label version 0.8.5 and earlier. It allows attackers with no account credentials to write files outside the server's designated storage folder. The weakness exists in components that handle uploaded images and labels, where file identifiers from callers are appended to storage paths without validation that the resulting location remains within approved directories.
How the attack unfolded
Amazon reconstructed the incident after discovering the attacker's Cairn control panel exposed on the internet without password protection. Cairn is an open-source framework that operates AI agents as automated penetration testers. The exposed panel revealed task settings, prompts, and complete run history.
Over roughly 48 hours, the agents progressed from initial reconnaissance to root access. In a separate session following the initial file-write capability, the agents exploited the same flaw to plant a file that Python executes automatically at startup. They then triggered a training feature that launched a new Python process, which loaded the malicious file and established a reverse connection to the attacker with root privileges.
Investigators attribute the campaign to a China-linked actor with moderate confidence, citing Simplified Chinese prompts, China Standard Time settings, and target selection likely aligned with Chinese interests. They have not connected the activity to a named threat group or confirmed state sponsorship.
Why it matters
This incident represents a significant evolution in offensive cyber capabilities. Autonomous AI agents demonstrated the ability to discover, analyze, and weaponize a zero-day vulnerability with minimal human intervention—a process that traditionally requires skilled security researchers. The 11-minute timeline from reconnaissance to exploitation capability suggests these tools can dramatically accelerate attack cycles. For organizations running vulnerable software, the window between vulnerability existence and active exploitation may be shrinking faster than patch deployment cycles can accommodate.
No patch available yet
Maintainers confirmed the flaw and merged a source code fix on October 19 that forces uploads to resolve inside approved folders and rejects problematic filenames. However, no patched release version is available for installation. The newest listed release remains version 0.8.5 from 2024.
The vulnerability now carries the identifier CVE-2026-133968 with a critical severity rating of 9.8 out of 10.
Immediate mitigation steps
With no fixed release available, organizations should block untrusted network access to MONAI Label servers using firewall and routing rules. The software runs with authentication disabled by default, which should be enabled immediately. Servers should run under limited accounts rather than root, with restricted write permissions.
Administrators should not assume source builds are safe without confirming they include the October fix. Systems that were network-accessible should be checked for unexpected Python startup files and unusual training jobs, the attack path used in the reported intrusion.
MONAI Label is a server application used by research teams to label medical scans and train imaging models, separate from the broader MONAI framework.
These details were first reported by Amazon Threat Intelligence in their incident analysis this week.