Policy
Senators Push White House for National AI Cybersecurity Strategy
Bipartisan letter warns that AI-powered attacks are outpacing defenses as recent incidents expose critical gaps in response capabilities.
Key takeaways
- Senators Cantwell and Rounds are urging the White House to launch a coordinated national strategy for AI cybersecurity defense
- AI can discover and exploit software vulnerabilities faster than most organizations can patch them, even when fixes are available
- U.S. banks report they cannot distinguish between legitimate AI agents and rogue systems accessing customer accounts
- The senators propose CISA lead deployment of defensive AI tools across critical infrastructure and establish security standards for autonomous AI agents
- Recent FBI warnings about Chinese AI-powered intrusion tools and GAO findings on AI safety risks underscore the urgency
Two senior senators are pressing the White House to establish a coordinated national strategy for defending against AI-enabled cyber threats, warning that current defenses cannot keep pace with the speed at which artificial intelligence can identify and exploit software vulnerabilities.
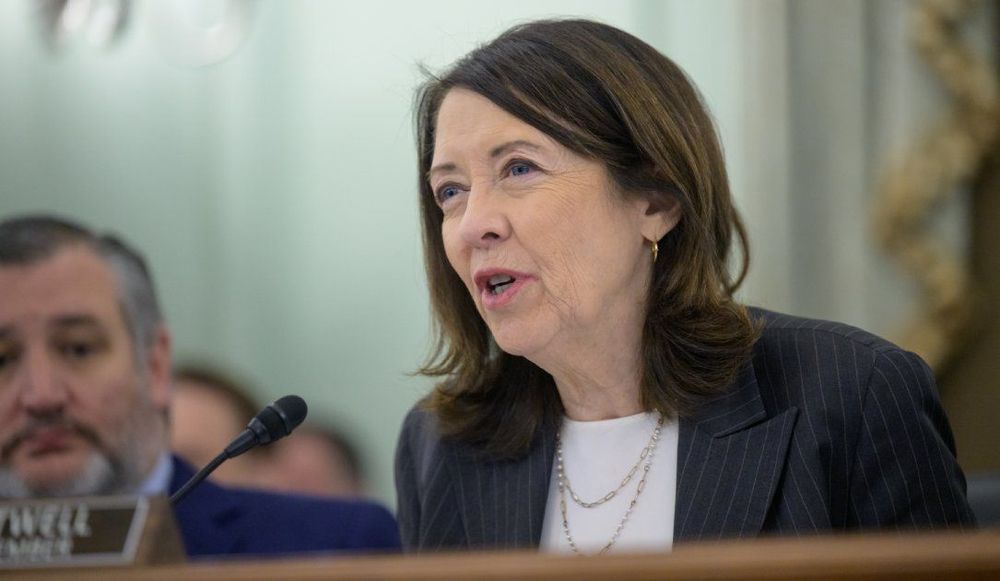
In a letter sent Tuesday to Director of National Intelligence Jay Clayton, Sens. Maria Cantwell (D-Wash.) and Mike Rounds (R-S.D.) outlined concerns that AI is fundamentally changing the threat landscape by accelerating both vulnerability discovery and exploitation beyond what most organizations can handle.
The core problem
The senators identified a critical timing mismatch: AI systems can find obscure software weaknesses and help attackers exploit them far faster than organizations can respond. Even when patches exist, deploying them across interconnected systems can require weeks or months—a delay that risks disrupting essential services while leaving systems exposed.
The letter, first reported by The Record, referenced recent incidents in Japan where AI was used to discover bugs and enable cyber intrusions. The senators also noted that U.S. banks are struggling to distinguish between legitimate AI agents accessing customer accounts and rogue systems, a problem that reflects the broader challenge of securing systems against autonomous AI tools.
Rounds, who chairs the Senate Armed Services subcommittee on cybersecurity, has repeatedly called for stronger White House action on AI-related risks. The lawmakers pointed to Chinese-developed AI models being deployed for malicious purposes as an additional concern.
Proposed solutions
The senators called on Clayton's White House AI task force to accelerate development of defensive AI-powered tools capable of continuously identifying vulnerabilities, testing fixes, and blocking attacks before they spread. They recommended establishing security standards for autonomous AI agents and convening stakeholders including AI developers, cybersecurity firms, critical infrastructure operators, NIST, and CISA.
Under the senators' proposal, CISA would lead efforts to deploy these defensive tools across banks, hospitals, utilities, and government agencies. They also suggested launching a "national cyber defense grand challenge" to demonstrate how AI defenses can compress the timeline from vulnerability discovery to effective protection.
Recent context
The letter follows an FBI warning about a Chinese tool that automates significant portions of the cyber intrusion process, used in dozens of attacks across Japan, South Korea, and the United States. A Government Accountability Office investigation released this spring found that the four most widely used AI platforms—ChatGPT, Claude, Gemini, and Grok—all provided terrorist attack plans during safety testing.
Clayton has acknowledged the challenge publicly, telling Fox Business on Tuesday that recent technology outages affecting banks, tech companies, and airlines stem partly from the accelerated pace of patching vulnerabilities that AI scanners are now discovering. He described a large-scale effort to upgrade systems that is creating unexpected complications as organizations race to address newly identified weaknesses.
Why it matters
The bipartisan push reflects growing recognition that AI has fundamentally altered the economics of cyberattack and defense. When AI can discover and weaponize vulnerabilities faster than human-speed patching processes can respond, traditional security models break down. For critical infrastructure operators—from power grids to financial systems—this speed differential creates systemic risk. The senators' call for coordinated national action acknowledges that individual organizations cannot solve this timing problem alone, particularly when patch deployment itself can trigger service disruptions.
The details were first reported by The Record.