US Accuses China of Distilling American AI Models Since 2024
Joint federal advisory alleges industrial-scale extraction of capabilities from Claude, GPT, Gemini, and Grok as Trump-Xi talks loom.
Federal Agencies Allege Systematic AI Capability Extraction
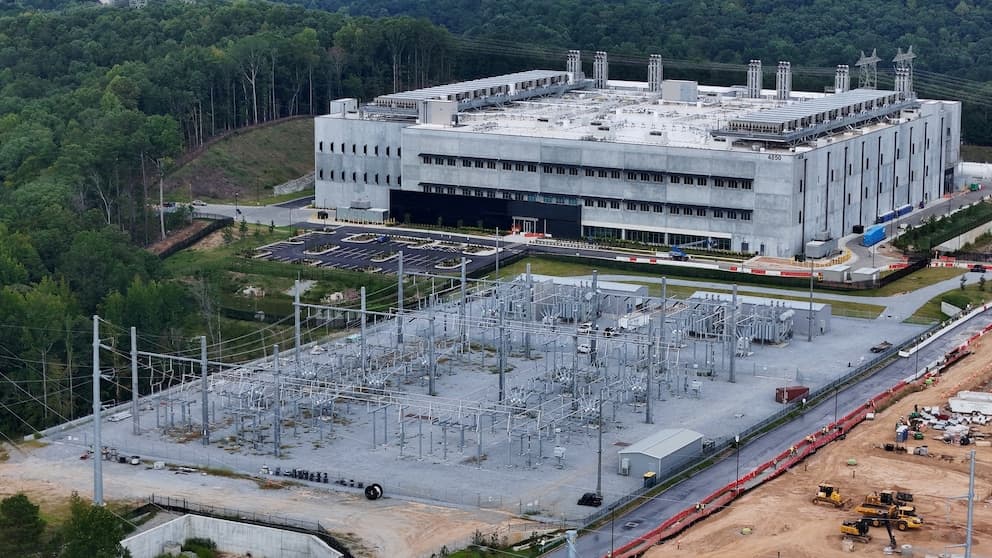
The FBI, National Security Agency, and Cybersecurity and Infrastructure Security Agency issued a joint cybersecurity advisory Tuesday accusing Chinese artificial intelligence developers of extracting capabilities from advanced American AI systems through a process known as distillation. According to the advisory, Chinese entities have targeted some of the most sophisticated AI models available, including Anthropic's Claude, OpenAI's GPT, Google's Gemini, and SpaceXAI's Grok, in efforts the agencies characterized as "aggressive, malicious" and operating at industrial scale.
The alleged activity has been ongoing since at least late 2024, according to the three-agency statement. China responded Wednesday, rejecting the U.S. claims, according to reporting first published by the Associated Press.
What Is AI Distillation
AI distillation refers to techniques that allow developers to extract knowledge and capabilities from a large, complex AI model and transfer them to a smaller or different system. While distillation has legitimate research applications, the federal advisory suggests Chinese developers are using these methods to replicate proprietary capabilities without authorization, potentially circumventing the substantial investment and technical expertise required to develop frontier AI systems independently.
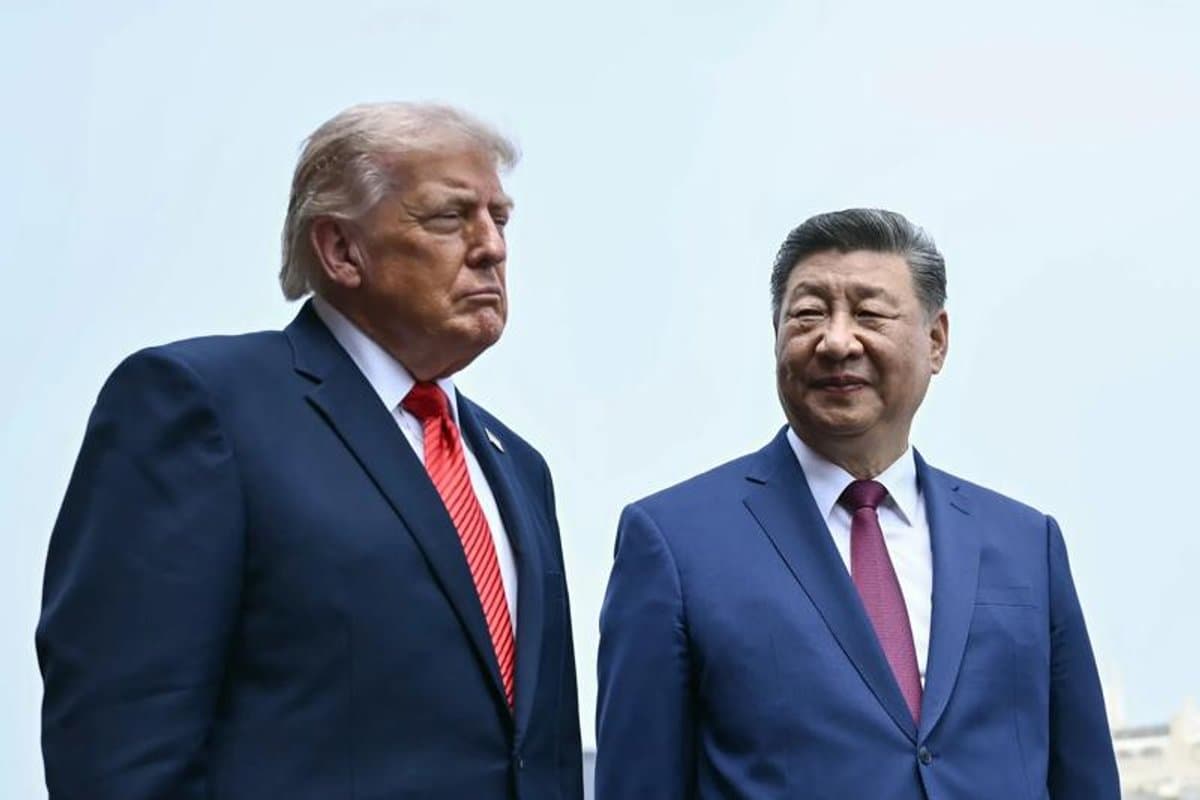
The timing of the advisory is notable, coming as AI governance is expected to feature in planned discussions between U.S. President Donald Trump and Chinese leader Xi Jinping.
Why It Matters
The distillation allegations represent a new front in U.S.-China technology competition, moving beyond traditional concerns about data theft or hardware restrictions to focus on the extraction of AI model capabilities themselves. If Chinese developers can systematically replicate the performance of models that cost hundreds of millions of dollars to train, it could undermine the competitive advantages of American AI companies and accelerate China's progress in artificial intelligence—potentially without the safety testing and alignment work that frontier labs conduct. The issue also complicates efforts to establish international AI governance frameworks, as any agreements would need mechanisms to prevent capability transfer through distillation.
The Associated Press first reported China's response to the U.S. allegations from Bangkok on September 10, 2026.
This is an original analysis by the Omega editorial team. Source reporting: AI Watch.
Want systems like this working for your business?
Book a Call