Rockwell Automation Patches Critical ICS Controller Flaws
Multiple vulnerabilities across Logix controllers, FactoryTalk products, and RSLinx software enable DoS attacks, authentication bypass, and unauthorized access.
Rockwell Automation Patches Critical ICS Controller Flaws
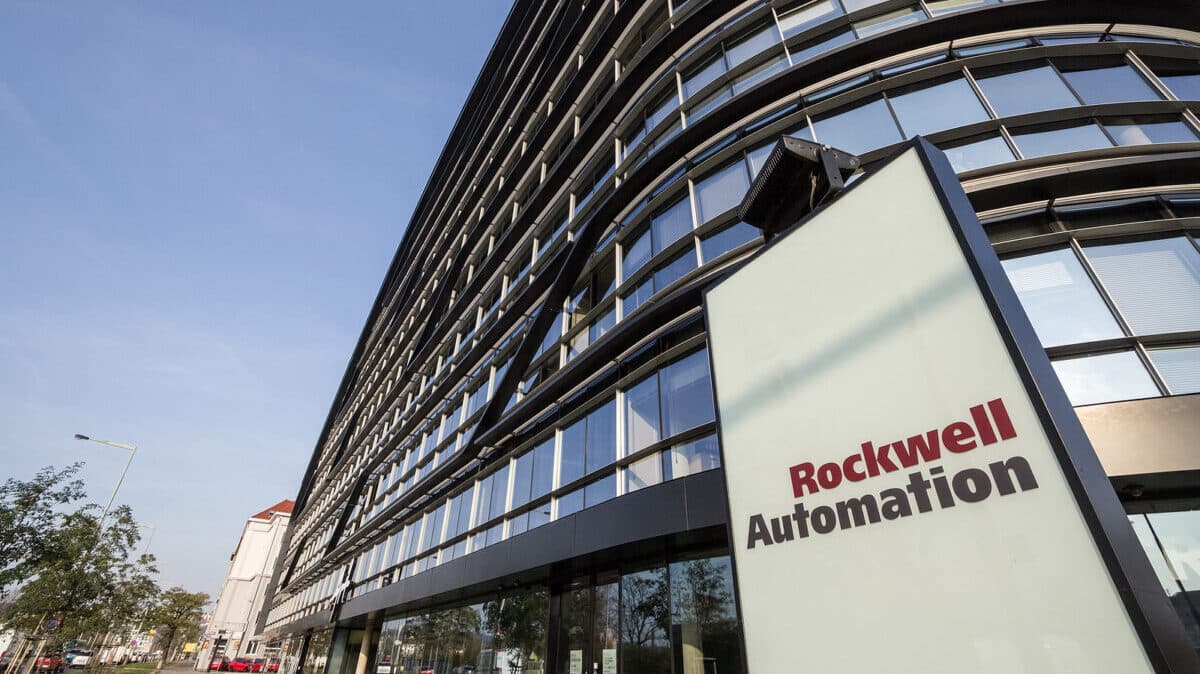
Rockwell Automation released security updates Tuesday addressing multiple vulnerabilities across its industrial control system product lines, including critical flaws that could allow unauthenticated attackers to take over devices and disrupt operations.
The patches cover vulnerabilities in Logix and CompactLogix controllers, Flex I/O dual-port Ethernet/IP adapters, RSLinx industrial communication software, and the FactoryTalk automation suite, according to details first reported by SecurityWeek.
Critical Password Reset Vulnerability
The most severe issue affects Flex I/O dual-port Ethernet/IP adapters, where a critical vulnerability allows unauthenticated attackers to change a device's web interface password. This flaw could enable unauthorized access and complete account takeover of affected industrial equipment.
The same Flex I/O adapters are also affected by a separate denial-of-service vulnerability that could disrupt operations.
Controller and FactoryTalk Issues
Rockwell addressed a high-severity DoS vulnerability in several controller models, including CompactLogix, ControlLogix, Compact GuardLogix, and GuardLogix systems. This flaw can trigger a major, non-recoverable fault that requires running a special recovery program to restore functionality. Some CompactLogix controllers face two additional DoS vulnerabilities.
The FactoryTalk Historian Site Edition received patches for three high- and critical-severity vulnerabilities enabling authentication bypass and DoS attacks. Meanwhile, FactoryTalk Analytics PavilionX contains a high-severity API authorization flaw that permits unauthorized actors to execute privileged operations, including user and role management and other administrative functions.
Rockwell also patched a legacy DoS vulnerability in RSLinx that originated from a third-party component.
Why it matters
These vulnerabilities affect widely deployed industrial control systems that manage critical manufacturing and infrastructure operations. The critical password reset flaw is particularly concerning because it requires no authentication, giving attackers a straightforward path to compromise industrial networks. While Rockwell confirmed recent in-the-wild exploitation of an older vulnerability (CVE-2021-22681), the company stated none of these newly patched issues have been exploited yet—making immediate patching crucial before threat actors discover them.
No Active Exploitation Reported
Rockwell indicated that none of the newly addressed security vulnerabilities have been targeted by threat actors, though the company recently confirmed active exploitation of an older vulnerability tracked as CVE-2021-22681.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) distributed Rockwell's ICS advisories Tuesday, though the agency did not publish a separate advisory for the FactoryTalk Historian vulnerabilities.
Details of the vulnerabilities and patches were first reported by SecurityWeek.
This is an original analysis by the Omega editorial team. Source reporting: Automation Watch.
Want systems like this working for your business?
Book a Call